


Information Security Organization Structure (Mitsubishi Electric Group)
Information Security
Basic Policy
In order to respond to the threat of cyberattacks, which are rapidly becoming more sophisticated and diverse, the Mitsubishi Electric Group is continually working to strengthen its cybersecurity and governance of information management and operations.
We manage the information entrusted to us by customers, business partners, and other stakeholders of Mitsubishi Electric, as well as information assets such as sales information, technical information, and intellectual property, in accordance with our Information Security Policy.
Information Security Organization Structure
The Mitsubishi Electric Group’s information security framework designates the President & CEO as the Chief Officer responsible for information security management. Meanwhile, the Executive Officer in charge of Information Security appointed as the Officer, Information Security of MELCO*1 Group oversees the corporate division that manages information security as well as the business divisions. This enables us to promote policies and initiatives common across the Group while more effectively integrating operations tailored to the circumstances of each business. The Chief Information Security Manager, under the direction of the Officer, Information Security of MELCO Group, formulates Group-wide information security policies and plans and oversees related initiatives. The Chief Information Manager also ensures compliance with customer supply chain requirements, international standards, and industry best practices, while regularly reporting on overall activities. In each business division, General Managers, Information Security operate under the supervision of their respective Officer, Information Security to manage information security of their own divisions, including oversight of associated companies.
The Officer, Information Security of MELCO Group convenes regular Information Security Management Meetings with General Managers, Information Security to communicate and coordinate the formulation of Group-wide information security policies and the planning of related initiatives.
Each division is equipped with functions for information management: CSIRT,*2 PSIRT,*3 and FSIRT.*4 The Corporate Information Security Division is responsible for planning and promoting the Group’s information security mechanisms, rules, IT system security, and compliance with personal data protection laws and regulations. In the event of a security incident, this division collaborates with the relevant business divisions to make prompt and informed decisions based on operational circumstances, ensuring swift incident response.
For overseas associated companies, Regional Chief Information Security General Managers formulate information security policies, and plan, oversee, and promote measures in their respective regions, and coordinate all information security management activities. They also collaborate with the Chief Information Security General Manager in formulating information security policies and planning initiatives for the Mitsubishi Electric Group as a whole.
- 1 Mitsubishi Electric Corporation
- 2 Computer Security Incident Response Team
- 3 Product Security Incident Response Team
- 4 Factory Security Incident Response Team
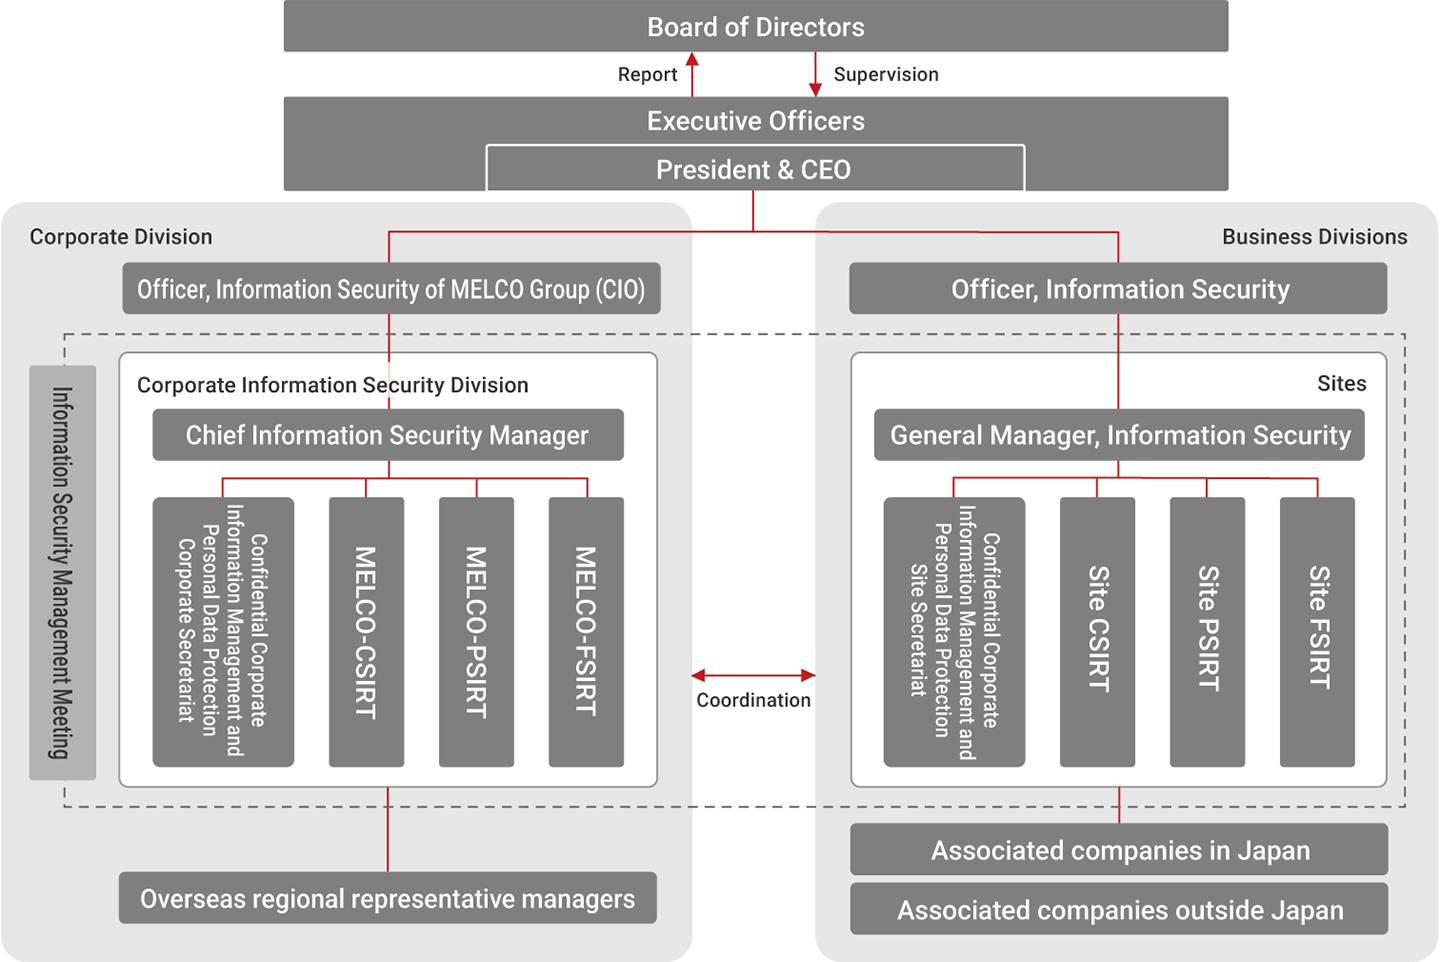
* CCI: Confidential Corporate Information
Personal Information Protection
Mitsubishi Electric has established the Personal Information Protection Policy and Company Rules on Personal Information Protection, developing a framework in accordance with the Japanese Industrial Standards JIS Q 15001: Personal Information Protection Management System – Requirements. Through this framework, the Company ensures thorough awareness of personal information protection among its employees and actively promotes initiatives to safeguard personal information.
In January 2008, we were granted the right to use the PrivacyMark, which certifies the establishment of management systems that ensure proper measures for personal information protection. We have been renewing the PrivacyMark certification since then. In January 2026, we completed the ninth PrivacyMark renewal process.
Cyberattack Countermeasures
To counter cyberattacks against companies, the Mitsubishi Electric Group is implementing centralized management of networks, computer terminals, and servers (cloud) and adopting defense-in-depth. Defense-in-depth provides protection against cyberattacks and enables the detection of suspicious activities and intrusions. The immediate response system we have established also helps to prevent and minimize damage.
In order to support work at the office as well as work requiring access from home or on a business trip, strong multifactor authentication has been introduced and authentications are centrally managed. Internet websites are constantly exposed to many external threats, and so we only launch websites that are approved in order to maintain a high security level.